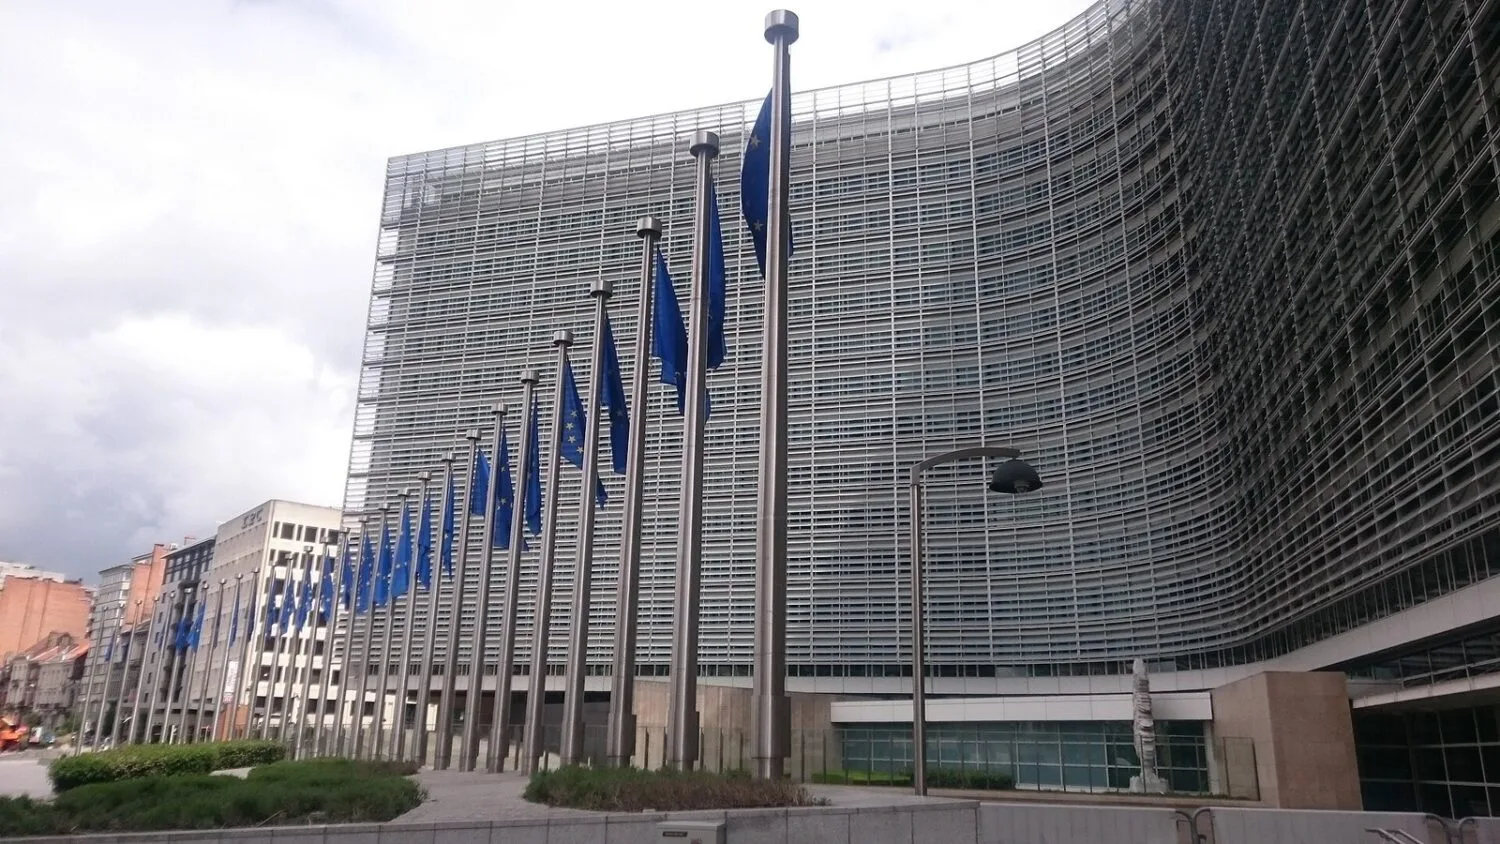
The European Commission has confirmed it was the target of a cyberattack. According to POLITICO’s findings, HR and medical expense reimbursement systems were down for about 10 days, and staff personal data may have been exposed.
The story was revealed on Thursday, 19 November, by POLITICO Europe, which had announced in a series of posts on X that it would report on a “major cyberattack” on the Commission.
What the Commission confirmed
Commission spokesperson Thomas Regnier told POLITICO that the Commission “has taken the necessary steps in response to a detected cyber campaign”. He added that individual systems were targeted and that, in line with standard practice, the people concerned were informed. According to the spokesperson, no evidence has been found of a data leak affecting the Commission’s entire staff.
Which systems were shut down
According to POLITICO, the disruption lasted about 10 days. Among the systems taken offline were Sysper, where staff check their payslips, record working time and submit leave requests, and MyPMO, which handles medical expense reimbursements. A source within the institution told POLITICO that investigators do not yet know whether staff data was actually accessed, and that the Commission believes it has contained most of the attack.
AI tool and the Commission’s response
According to POLITICO’s sources, CERT-EU, which protects EU institutions, determined that the attackers used ARTEX, a publicly available AI-powered penetration testing tool. The incident was discussed at an extraordinary meeting of the Corporate Management Board, the Commission’s highest internal governing body. On Wednesday, Commissioner for Technology Henna Virkkunen briefed the College of Commissioners on the situation. The matter was also discussed at the weekly meeting on 18 November.
It has not been disclosed who is behind the attack, how many employees are affected, or exactly what data may have been taken. Among the Commission’s staff are also citizens of Poland.
Earlier incidents
This is another incident this year. On 30 January, the Commission reported traces of an attack on the infrastructure managing mobile devices, which may have given access to the names and phone numbers of some staff. CERT-EU later also described a break-in to the Commission’s AWS cloud, linked to the TeamPCP group, which resulted in a data leak from services hosted on the Europa platform.